
Short answer: use a 6-digit OTP that is valid for 5 to 10 minutes, and allow 3 to 5 wrong tries. That suits most logins and signups in India. Payments and password resets can use a shorter time, and delivery OTPs can stay valid longer. This page explains how long an OTP should be valid and how many digits it should have, with a table by use case and the matching Fast2SMS Smart OTP settings.
Recommended OTP validity and length by use case
| Use case | Digits | Valid for | Wrong tries |
|---|---|---|---|
| Login | 6 | 5 to 10 minutes | 3 to 5 |
| Signup / number verification | 6 | 10 minutes | 3 to 5 |
| Payment confirmation | 6 | 3 to 5 minutes | 3 |
| Password reset | 6 | 5 minutes | 3 |
| Delivery OTP shared at the door | 4 to 6 | Until the delivery is done (hours or a day) | 3 to 5 |
| Cash on delivery order confirmation | 4 to 6 | 10 to 30 minutes | 3 to 5 |
These are common choices, not rules. Shorter is safer. Longer is kinder to users on slow networks. Pick what fits the risk of the action.
How many digits should an OTP have?
A 4-digit code has 10,000 possible values. A 6-digit code has 1,000,000. If you allow 5 tries, a person guessing has a 1 in 2,000 chance against 4 digits and a 1 in 200,000 chance against 6 digits. Six digits is still easy to read and type, which is why it is the usual choice.
Use 4 digits only when someone has to read the code out loud, like a delivery OTP, and the risk is low. Use 8 or more only when your own rules require it, because long codes cause typing mistakes.
How long should an OTP be valid?
The code should live just long enough for the message to arrive and the user to type it. Most users enter a code within a minute or two. A 5 to 10 minute window covers slow networks and app switching. Codes that stay valid for hours give more time for a leaked code to be misused.
Write the same time in the message, for example “Valid for 10 minutes”, so users know when to ask for a new code.
Set expiry, length and tries in Smart OTP
-
Set length and expiry in the Send OTP call
Pass
otp_length(4 to 10, default 6) andotp_expiryin minutes (1 to 10080, default 15). A length below 4 is changed to 6.{"mobile":"9999999999","otp_id":"YOUR_OTP_ID","otp_length":6,"otp_expiry":10} -
Match the minutes in your message
If your DLT template has a variable for the minutes, fill it with
variables_valuesso the text always matchesotp_expiry. The OTP variable itself is filled for you.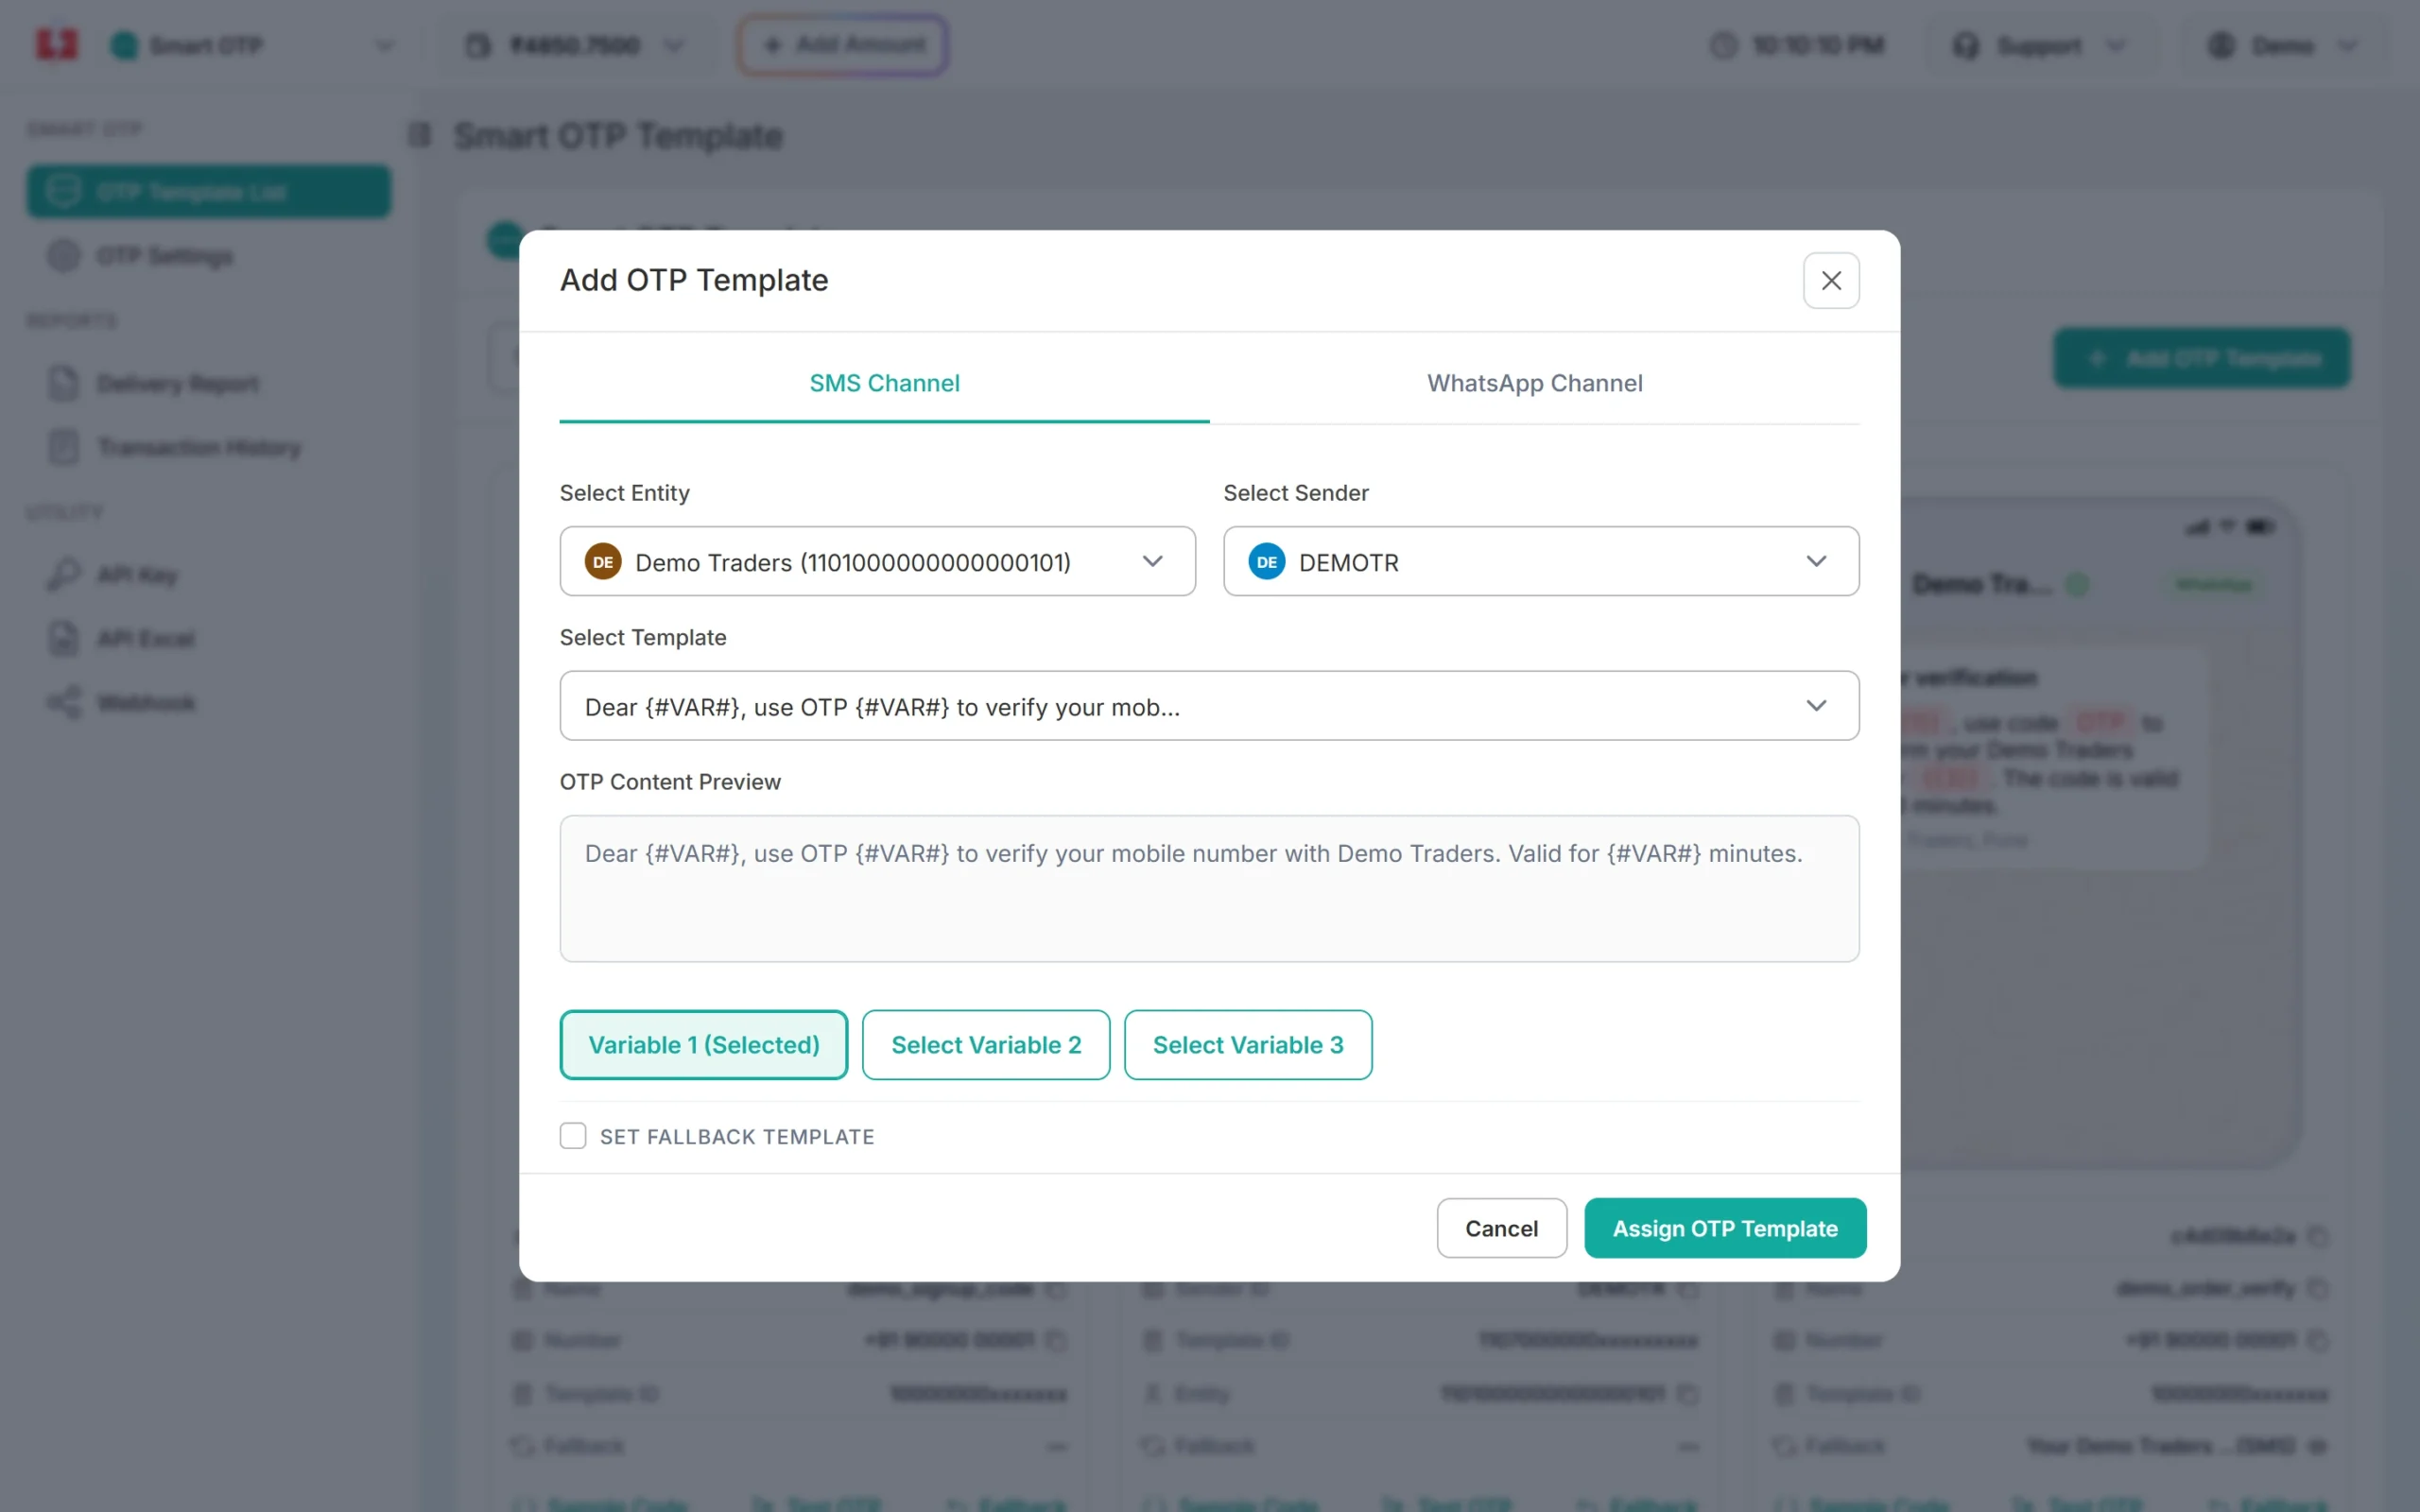
A template with a “Valid for {#VAR#} minutes” part. -
Set wrong tries and resend wait
In OTP Settings, set Max Verify OTP Limit (Per SMS) from 1 to 100 and SMS Resend / Time Limit (Seconds) from 0 to 3600. When the tries are used up, verify answers “Maximum verification attempts reached. OTP is no longer valid.”
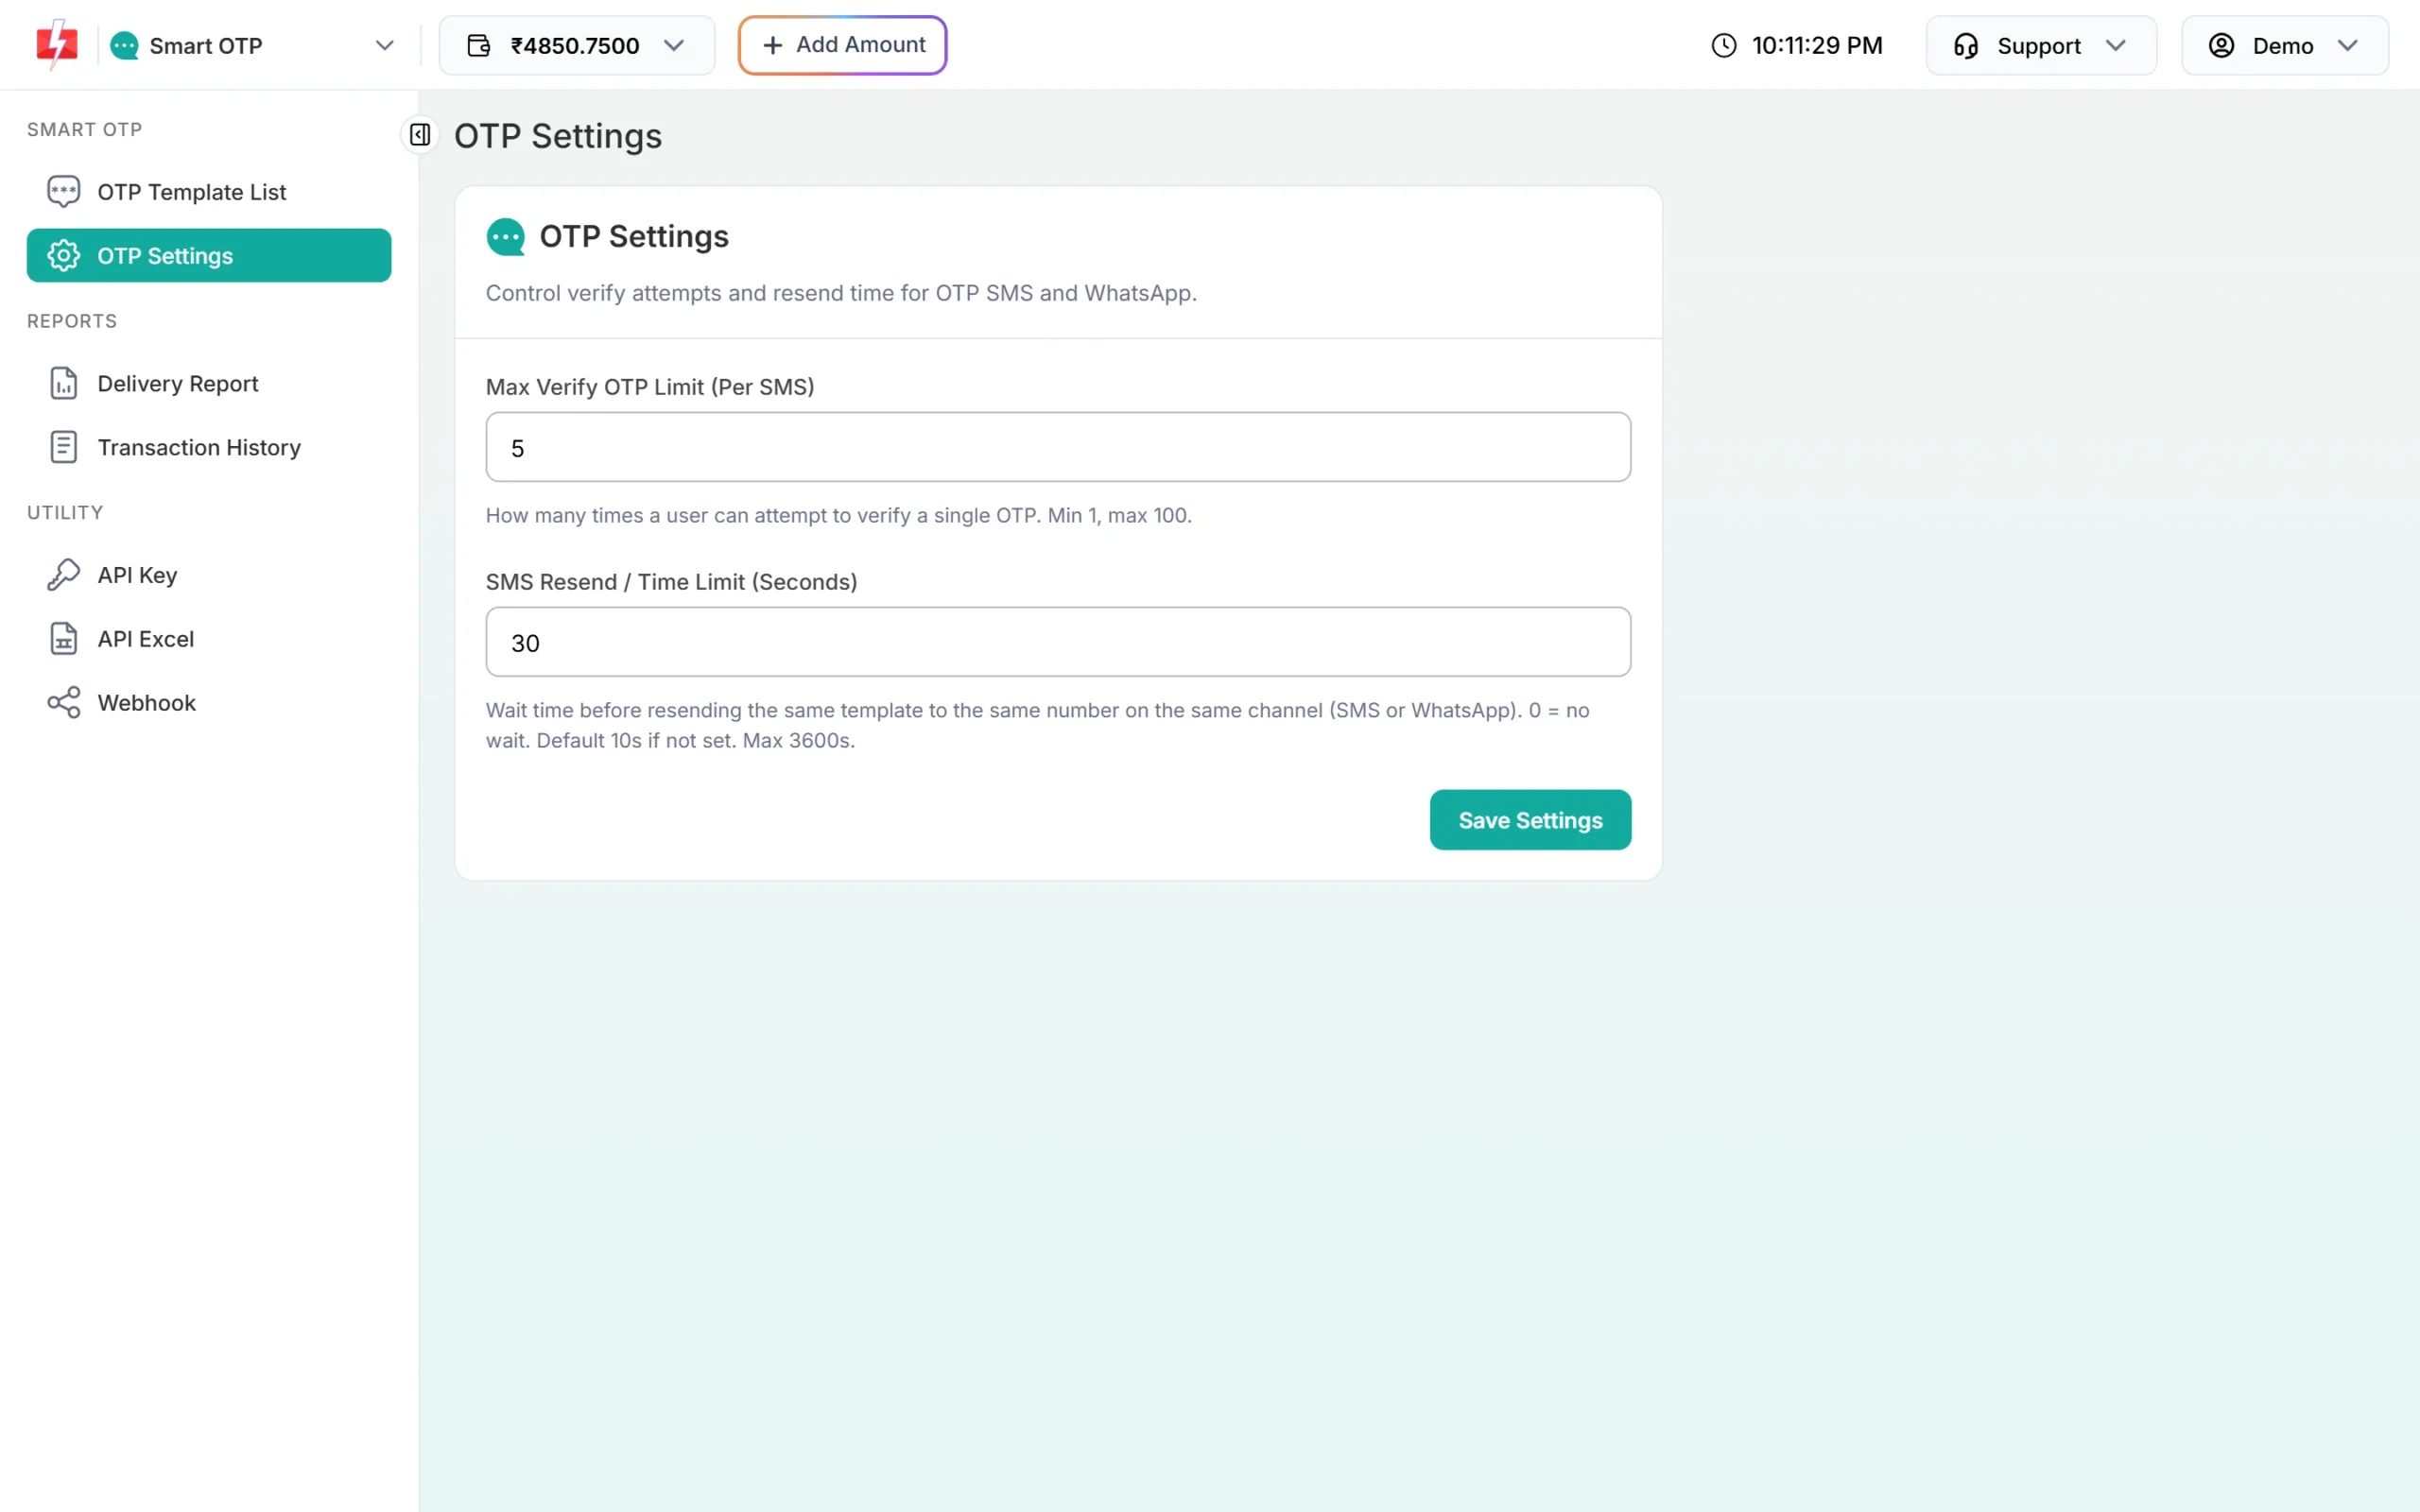
Account-wide limits for every OTP you send.
Frequently asked questions
What is the standard OTP validity time?
There is no single standard. 5 to 10 minutes is common for logins in India. Smart OTP uses 15 minutes if you do not set otp_expiry.
Is a 4-digit OTP safe?
It is weaker than 6 digits. With a low try limit it can be fine for low-risk uses like delivery codes. Use 6 digits for login and payments.
Can an OTP be valid for 24 hours?
Yes. otp_expiry accepts up to 10080 minutes (7 days). Use long validity only when the code is shared in person, such as at delivery.
Can I use my own OTP code?
Yes. Pass it in otp (up to 10 characters). Make it random, not based on time or a counter.
Does the WhatsApp OTP show an expiry?
WhatsApp Authentication templates can include an expiry line. Set it to the same minutes as otp_expiry.
Why does an OTP stop working before it expires?
A newer OTP to the same number cancels older ones. The code also stops working after the allowed wrong tries.