
You can add OTP verification to any HTML website or form with two lines: one script tag and one <div data-f2s-otp>. Visitors type their mobile number, get a code by SMS or WhatsApp through Fast2SMS Smart OTP, and your page gets a signed token once the number is verified. This guide shows the log-in box, the data-f2s-protect mode that makes an existing form wait for OTP, and the one server check (f2s_token) you must not skip.
Download the plain HTML OTP widget example (zip)Download .zip
Download the complete OTP widget kit (zip)Download .zip
How the OTP widget works
- Your page loads
f2s-otp-widget.min.js(one file, no other libraries). - The widget posts the mobile number to your own backend, for example
/f2s-otp. - Your backend checks its limits and then calls Fast2SMS Smart OTP with your API key and OTP ID.
- The visitor types the code. The backend verifies it and gives the page a signed, one-time token.
- Your form handler checks that token before it trusts the number.
The Fast2SMS API key never reaches the browser. Anything in a web page can be read by any visitor, so the key stays in the backend’s settings.
Before you start
- A Fast2SMS account with wallet balance.
- An approved DLT OTP template (for SMS) or an approved WhatsApp Authentication or Utility template.
- Somewhere to run one backend file: normal PHP hosting is enough, or Node.js, Python or a serverless host.
- Indian mobile numbers. Smart OTP sends to 10-digit numbers starting with 6 to 9.
Set up OTP verification on an HTML page
-
Create a Smart OTP template and copy its OTP ID
In the Fast2SMS panel, open Smart OTP > OTP Template List and click Add OTP Template. Pick SMS Channel with your approved DLT OTP template, or WhatsApp Channel with an approved Authentication or Utility template. You can add a fallback on the other channel. Then copy the 10-character OTP ID from the card. It decides the channel, the template and the fallback for every code the widget sends.
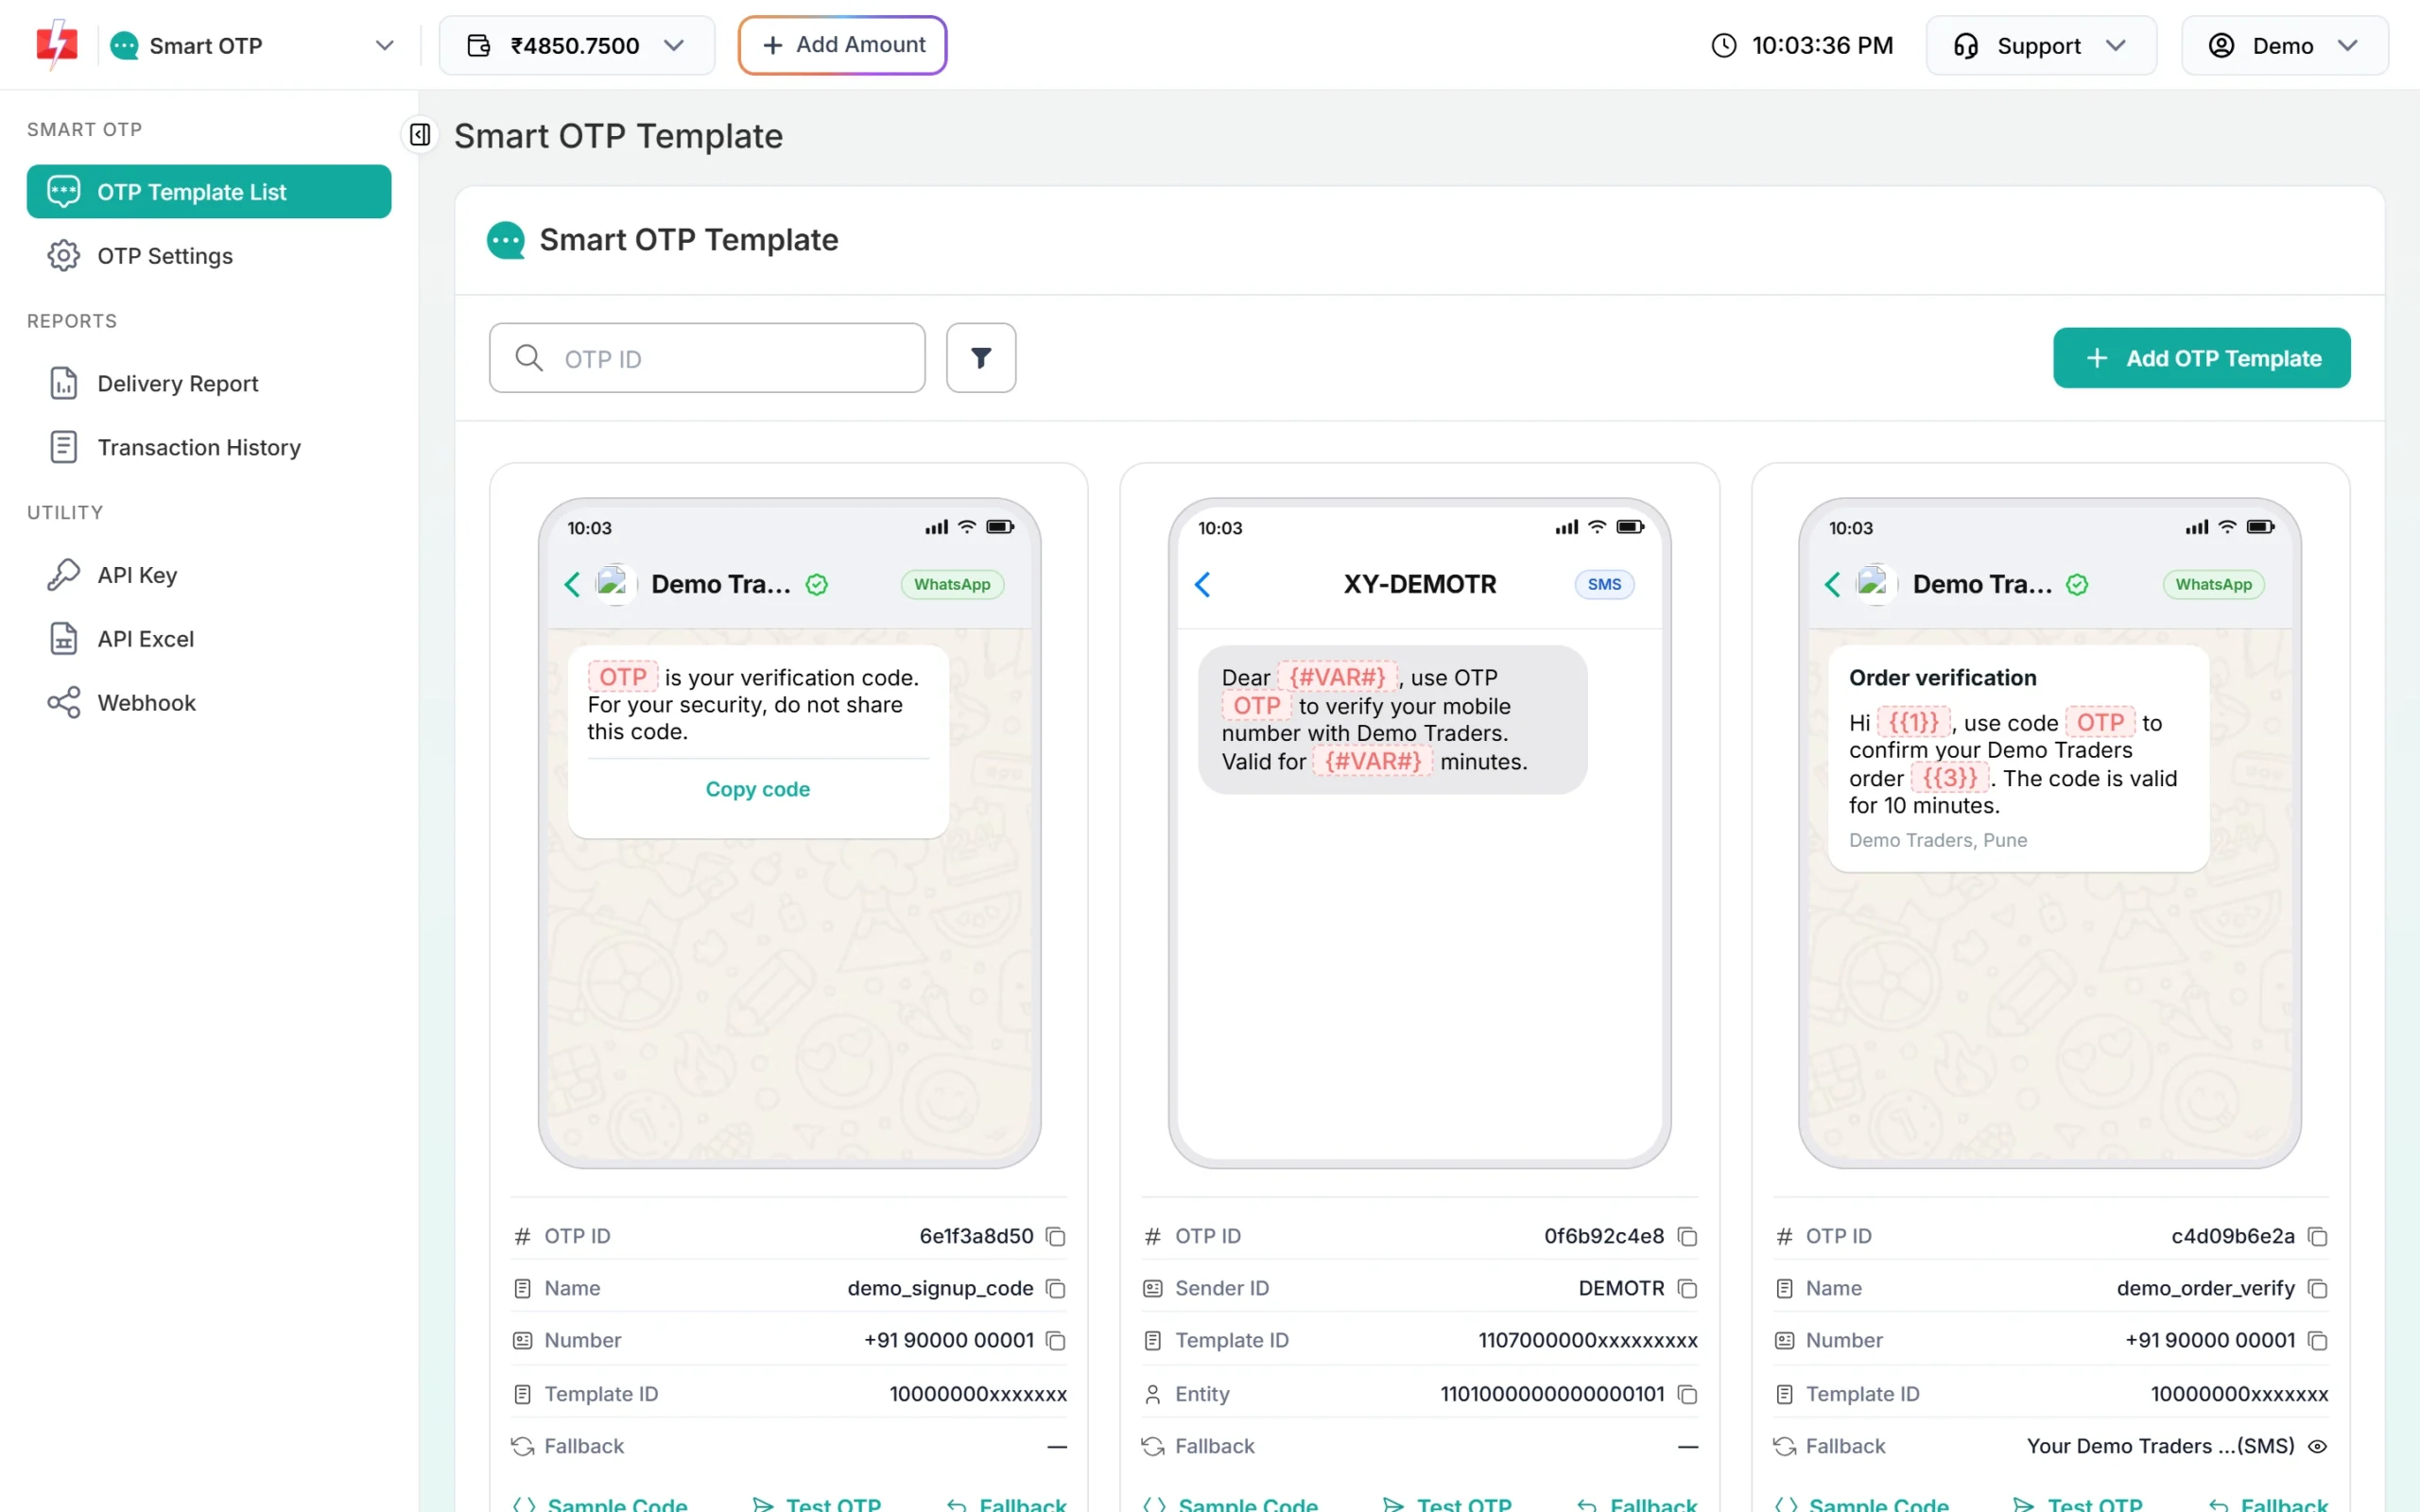
Copy the OTP ID from the template card. -
Run a backend that holds your API key
The widget never calls Fast2SMS. It calls a small backend that you run, and only that backend knows your API key. The full kit has ready backends for PHP hosting (one file), Node.js with Express, Python Flask, Django, Laravel, Cloudflare Workers, Vercel or Netlify functions and Google Apps Script (see the OTP widget overview). Copy the key from API Key under UTILITY in the panel, and give the backend these three settings:
FAST2SMS_API_KEY=YOUR_API_KEY F2S_OTP_ID=YOUR_OTP_ID F2S_TOKEN_SECRET=at-least-32-random-charactersF2S_TOKEN_SECRETis any random text of 32 or more characters. The backend will not start (or, on PHP and serverless hosts, refuses every request) if one of these is missing or wrong.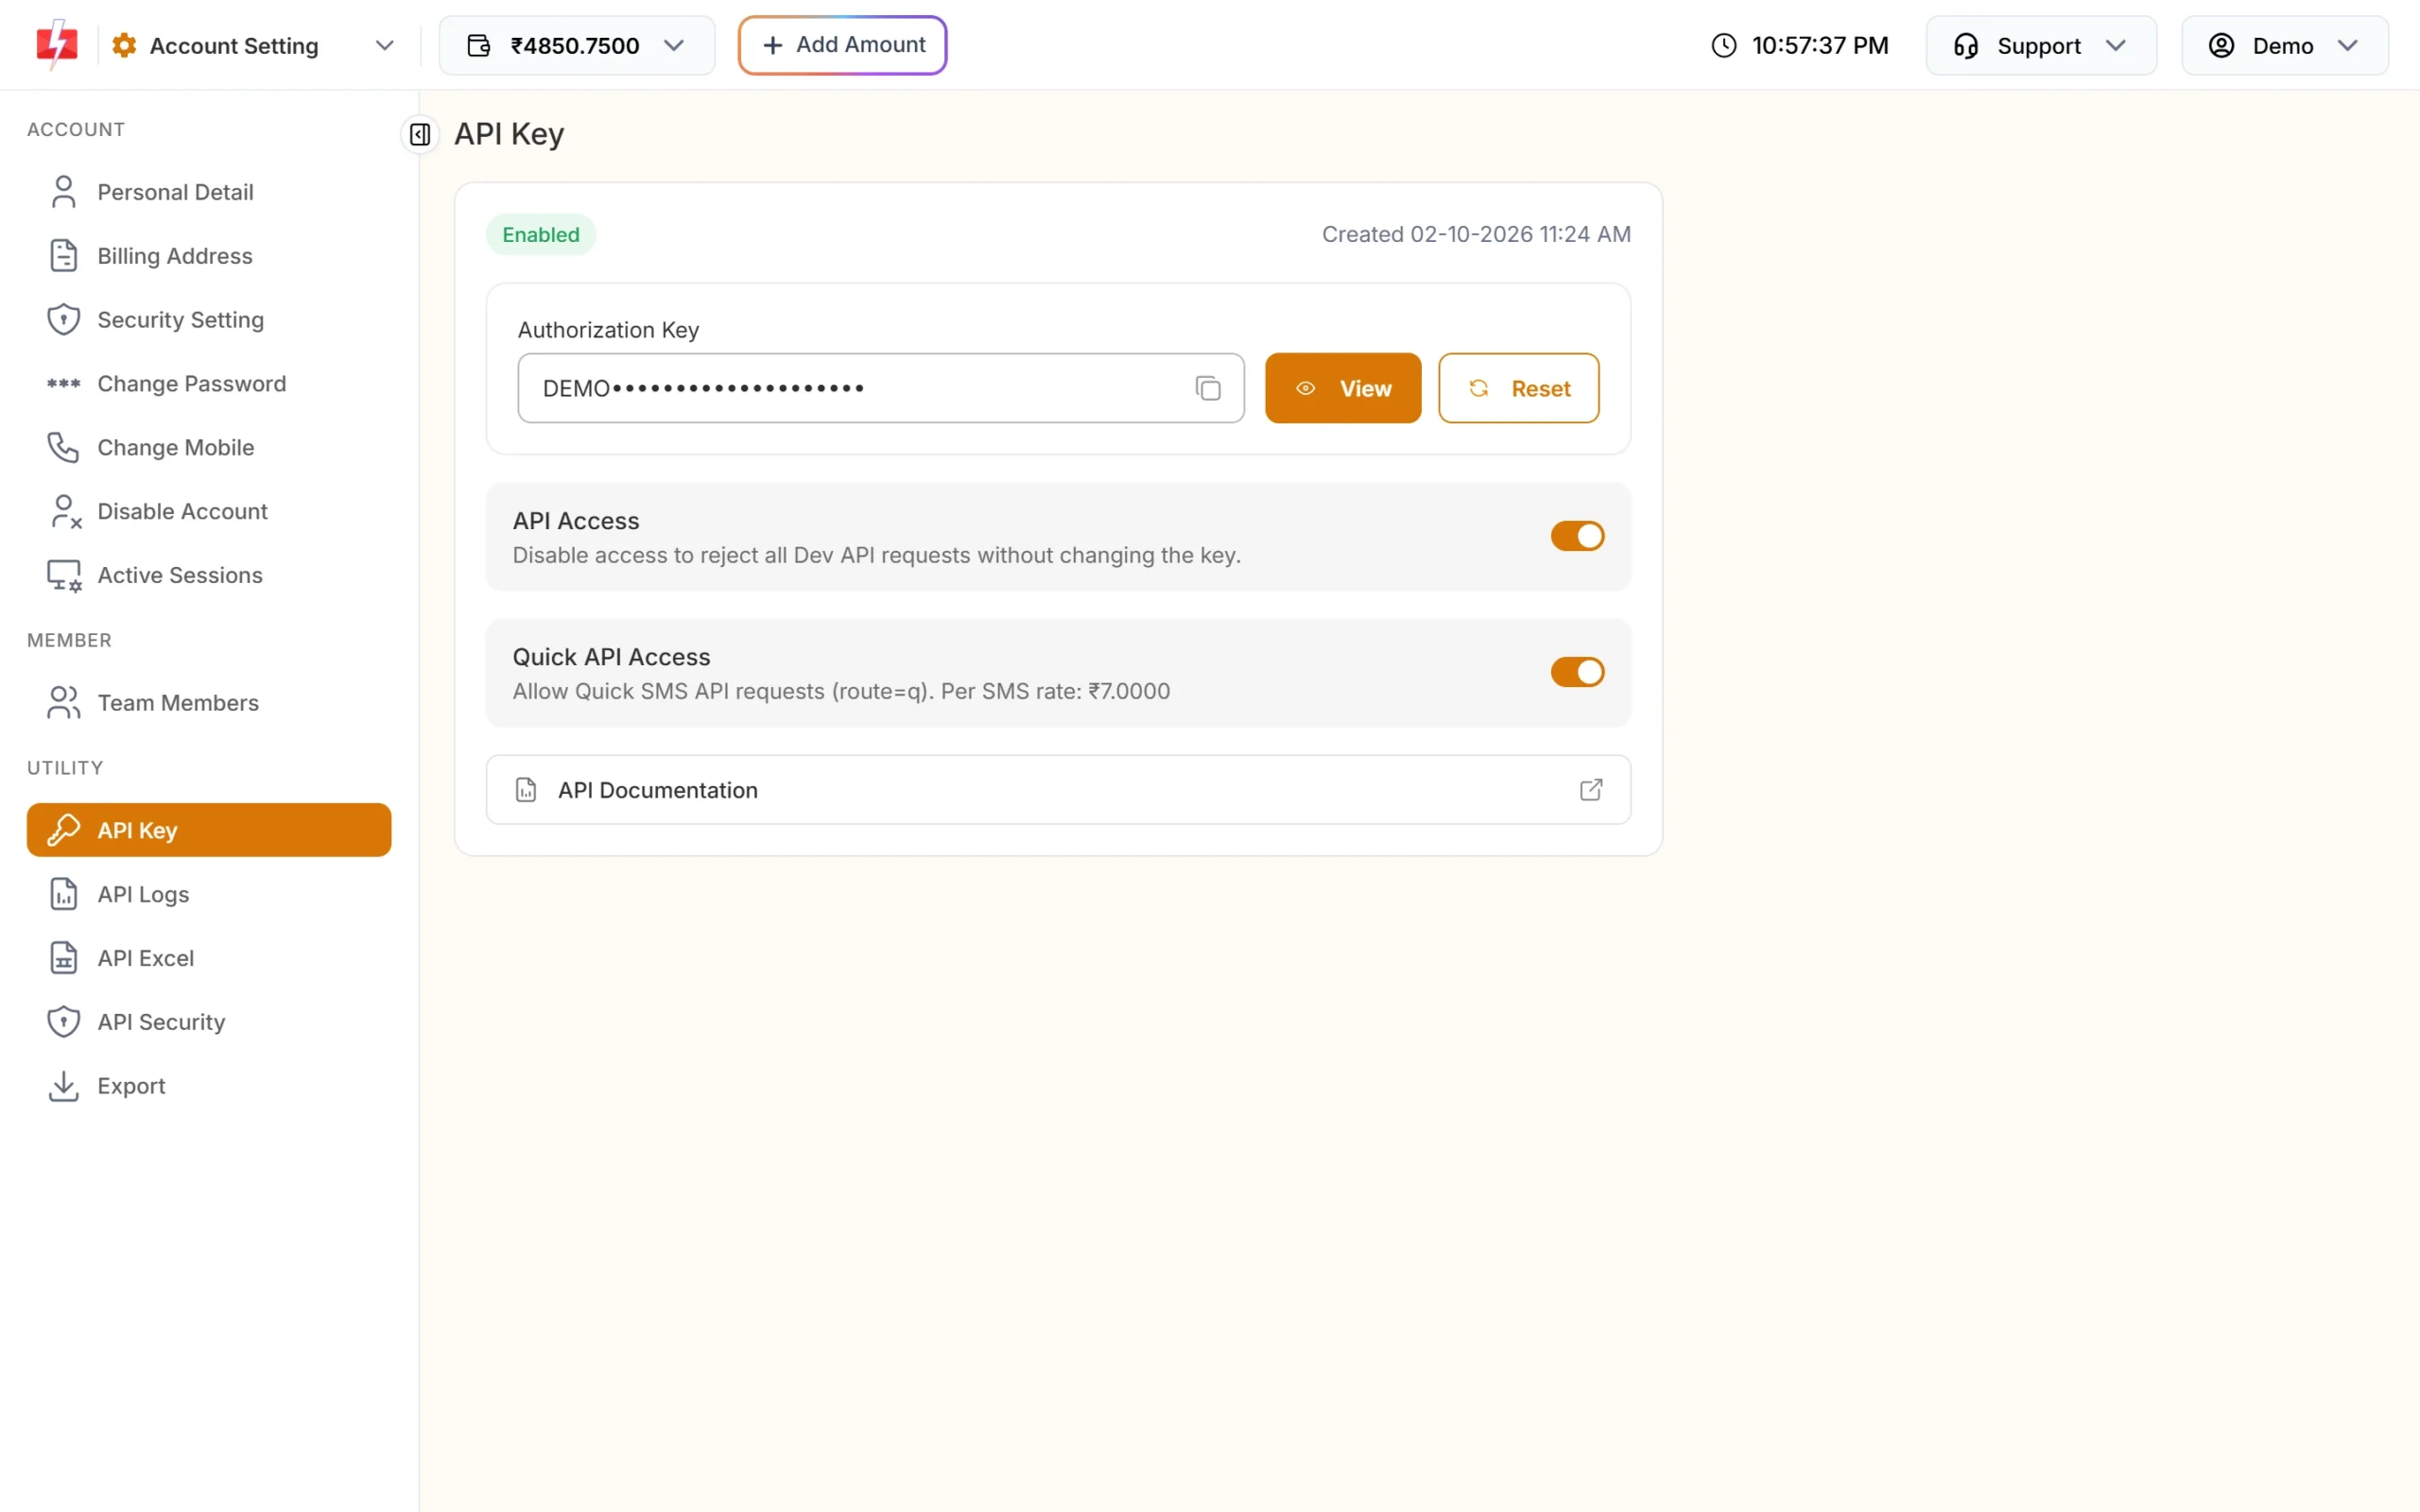
The key goes into your backend settings only. -
Add the two lines to your page
Copy
f2s-otp-widget.min.jsnext to your page and add:<script src="f2s-otp-widget.min.js" defer></script> <div data-f2s-otp data-endpoint="/f2s-otp" data-on-verified="onLogin"></div>data-endpointis your backend URL, never fast2sms.com. With the PHP kit it is/f2s-otp.php, on Vercel or Netlify/api/f2s-otp, and with the Cloudflare Worker kit the full Worker URL. The box shows a mobile field with +91 and a Send OTP button.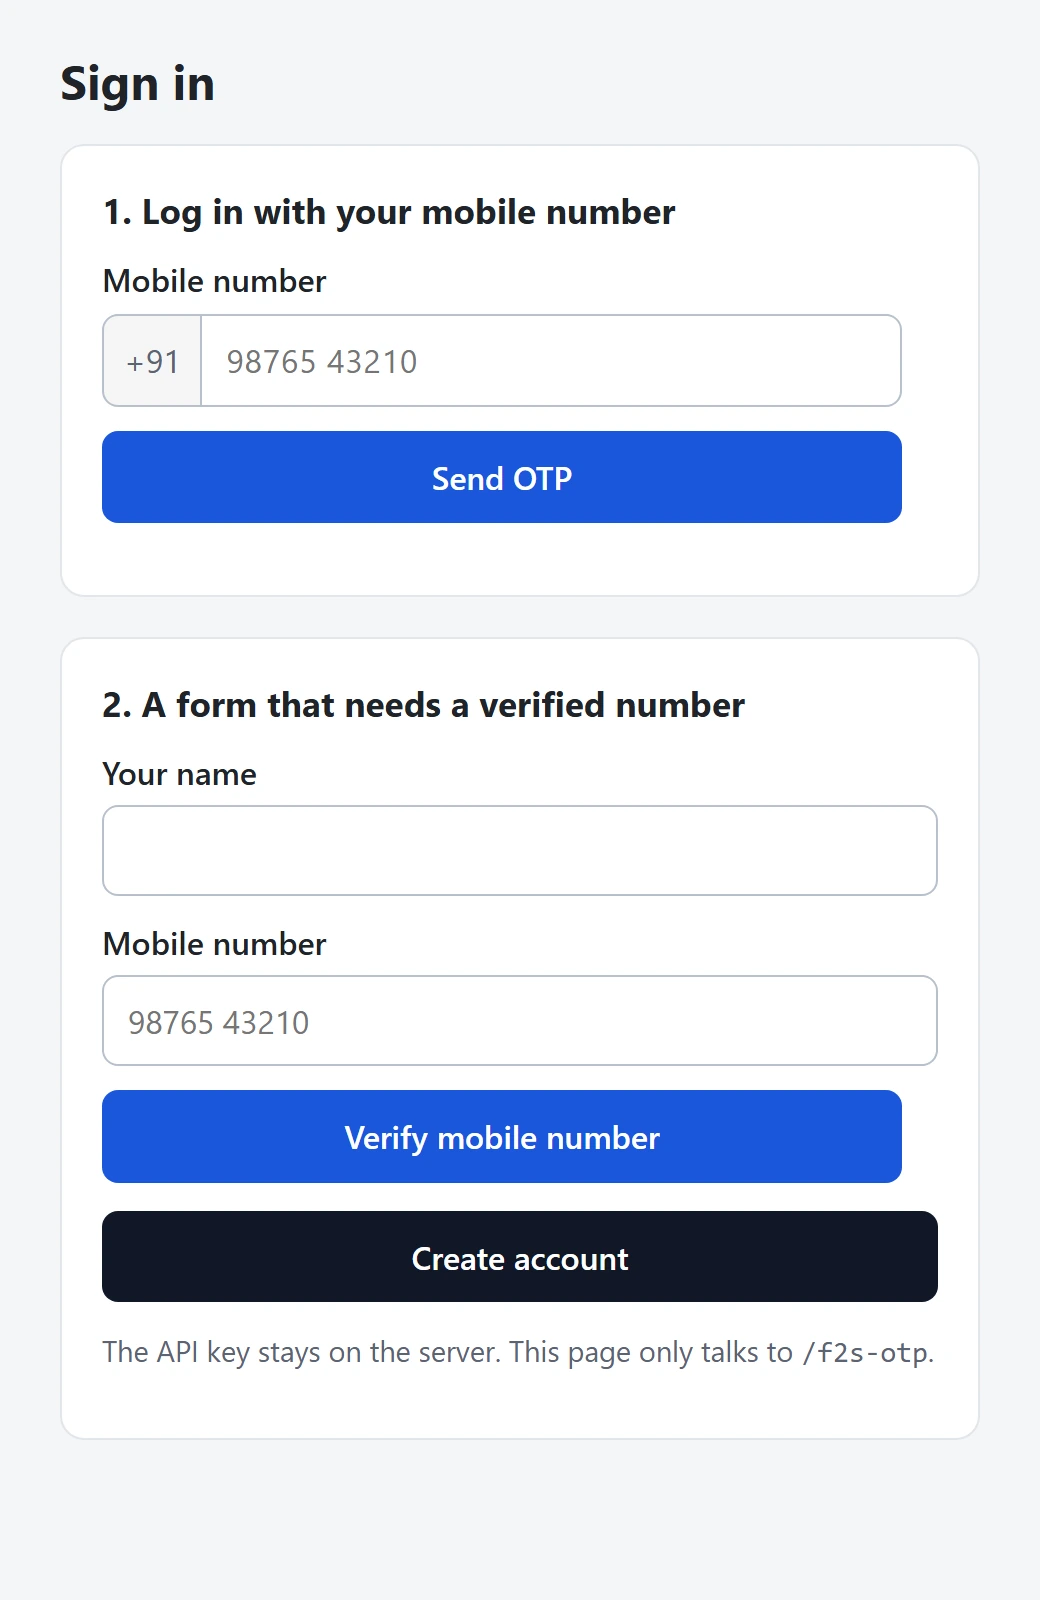
Top: the log-in box. Bottom: a form that needs a verified number. -
Send the token to your server
When the number is verified, the widget calls the function named in
data-on-verifiedwithtoken,mobile,maskedandexpiresIn. Post the token to your own log-in or sign-up route:<script> function onLogin(d) { fetch('/login', { method: 'POST', headers: { 'Content-Type': 'application/json' }, body: JSON.stringify({ f2s_token: d.token }) }); } </script>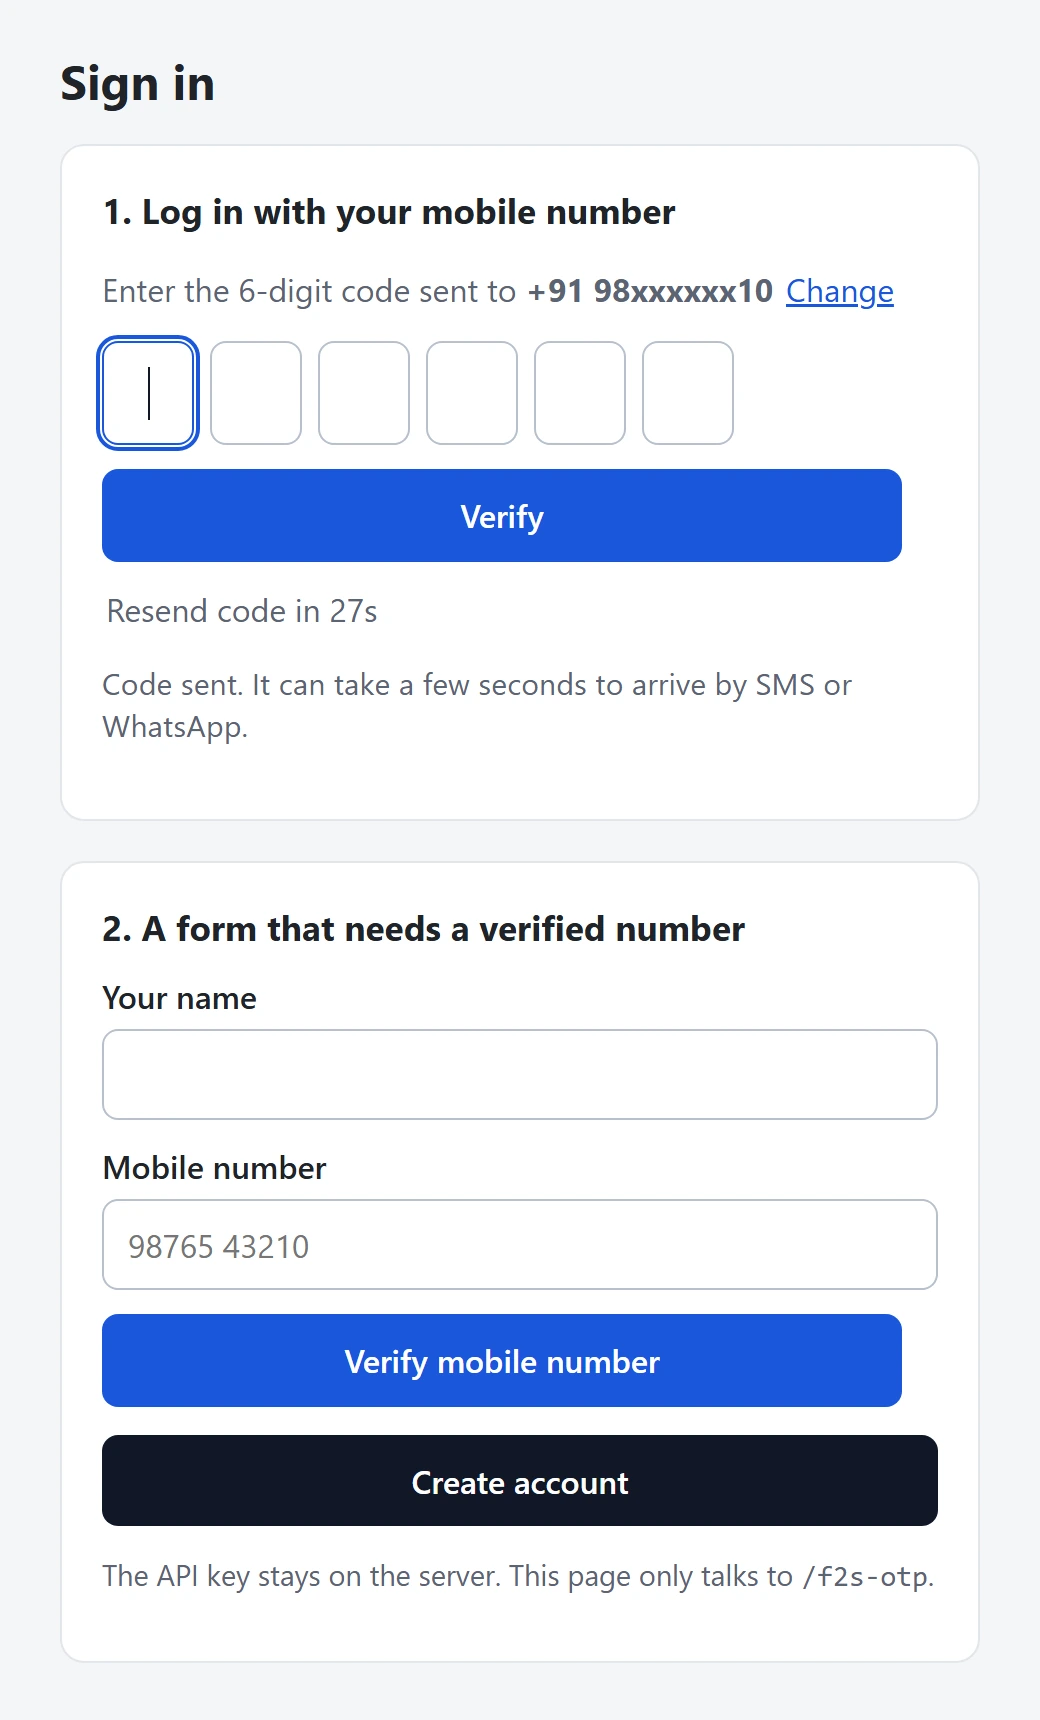
After Send OTP: six code boxes and a Resend countdown.
Make an existing form wait for OTP (data-f2s-protect)
If you already have a sign-up, enquiry or order form, you do not need a separate box. Add data-f2s-protect and data-endpoint to the <form> tag. The form then cannot be submitted until the number is verified, and the widget adds a hidden field named f2s_token.
<form action="/signup" method="post" data-f2s-protect data-endpoint="/f2s-otp" data-mobile-field="phone">
  <input name="name" required>
  <input name="phone" type="tel" required>
  <div data-f2s-slot></div>
  <button type="submit">Create account</button>
</form>data-mobile-fieldpoints at your own phone input. Without it, the widget shows its own phone field.data-f2s-slotmarks where the OTP box goes. Without it, the box goes just before the submit button.- If the visitor edits the phone field after verifying, the token is cleared and they verify again.
data-auto-submitsubmits the form right after verification.
Check f2s_token on the server
This step is the one that actually protects you. The hidden field stops normal visitors who skip the OTP, but a bot can post your form directly. Your form handler must check the token with the kit’s helper and reject the request if it fails. Use the number the helper returns, not the posted field.
// Node.js / Express backend kit
const v = await otp.verifyToken(req.body.f2s_token, { mobile: req.body.phone });
if (!v) return res.status(403).send('Mobile number not verified.');
// v.mobile is the verified 10-digit number. A token works only once.
<?php
// PHP single-file backend kit
require __DIR__ . '/f2s-otp.php';
$v = \F2sOtp\verify_token($_POST['f2s_token'] ?? '', $_POST['phone'] ?? null);
if ($v === null) { http_response_code(403); exit('Mobile number not verified.'); }
// $v['mobile'] is the verified 10-digit number.The helper checks the signature, the expiry (10 minutes by default) and that the token belongs to that number. A token works only once.
Useful attributes
| Attribute | What it does |
|---|---|
data-endpoint |
Your backend URL (required). |
data-otp-id |
Use another OTP ID, for example a WhatsApp-only template. The backend accepts it only if it is in its F2S_OTP_IDS list. |
data-title |
A heading above the box. |
data-send-text, data-verify-text |
Button texts (default Send OTP and Verify). |
data-token-name |
Name of the hidden field on a protected form (default f2s_token). |
data-captcha, data-captcha-sitekey |
Turnstile or reCAPTCHA, when the backend has F2S_CAPTCHA on. |
Colours and sizes are CSS variables, for example .f2s-otp { --f2s-primary: #0f766e; --f2s-radius: 4px; }. The first code box has autocomplete="one-time-code", so phone keyboards can offer the code from the SMS, and a pasted code fills all the boxes.
Where to paste it on a site builder
- Webflow: the script in Page settings > Custom code (before
</body>), the<div>in an Embed element. - Wix: put the script and the
<div>in the same Embed HTML element, and use the fullhttps://backend URL. - Backend on another domain: add your site’s origin to the backend’s
F2S_ALLOWED_ORIGINS, for examplehttps://www.example.com.
Limits and cost
The backend checks these limits before it makes any paid call. Change them with settings, not code.
| Backend setting | Default | What it does |
|---|---|---|
F2S_RESEND_WAIT |
30 seconds | Wait between two sends to one number. |
F2S_LIMIT_PER_NUMBER |
5 per hour | Sends to one mobile number. |
F2S_LIMIT_PER_IP |
20 per hour | Sends from one IP address. |
F2S_LIMIT_VERIFY_PER_IP |
60 per hour | Verify calls from one IP address. |
F2S_MAX_VERIFY |
5 | Wrong codes allowed for one code. |
F2S_TOKEN_TTL |
600 seconds | How long the verified token lasts. |
F2S_CAPTCHA |
off | turnstile or recaptcha, with F2S_CAPTCHA_SECRET. |
Resend sends the same code again. Fast2SMS allows it within 10 minutes of the first send, up to 5 sends in total. Sending a fresh code for a number cancels the older code. If the template has a fallback and the first channel fails, Fast2SMS sends the same code once on the other channel.
Each send and each resend is charged at your Smart OTP rate. Verify is free. If a fallback message goes out on the second channel, that message is charged too, and so is a Test OTP from the template card, because it is a real send. See the current rates on the Smart OTP page.
Sending in bulk? For high OTP volumes our team offers discounted rates. Talk to our team or see OTP pricing.
How this example was tested
This page is the demo page of every backend in the kit. It was run in headless Chrome against the PHP, Node.js, Python Flask, Django, Cloudflare Worker, Vercel and Netlify backends, 47 checks each, against a test server that answers like Fast2SMS. No real SMS was sent in these tests, so do one live send with your own template before you go live.
Common problems and fixes
| What the visitor sees | Why | Fix |
|---|---|---|
| “This page is not allowed to use this OTP service.” | The page is not on the backend’s domain or in F2S_ALLOWED_ORIGINS. |
Add the exact origin (https:// plus domain, no path). |
| “We could not send the code right now.” | An account problem: API key, OTP ID, wallet balance or template. | Read the backend log. It names the real reason. |
| “Could not reach the server.” | Wrong data-endpoint, backend down, or CORS. |
Open the endpoint URL and check the browser console. |
| Nothing shows | The script did not load, or data-f2s-otp is missing. |
Check the script path. For a div added later, call Fast2smsOtp.init(). |
| “Code sent” but no SMS | Sent means Fast2SMS accepted it, not that the phone got it. | Check Smart OTP > Delivery Report. |
Frequently asked questions
Can I add OTP verification to a website without a backend?
No. Some server has to hold the API key, because a key in a web page can be copied by anyone. If you have no server, the kit’s Cloudflare Worker backend works on Cloudflare’s free tier, a Vercel or Netlify function is another option, and the Google Apps Script backend gives you a hosted form.
Does the widget work with WhatsApp OTP?
Yes. The channel comes from your OTP ID. If its template is on WhatsApp, or has a WhatsApp fallback, the same widget is used and the visitor gets the code on WhatsApp.
What is f2s_token?
It is a hidden field the widget adds to a protected form after verification. It holds a signed token that proves the number was verified a moment ago. Your server checks it with the kit’s helper; the token works once and lasts 10 minutes by default.
Is the OTP widget free?
The kit is free under the MIT license. You pay only for the OTPs you send from your Fast2SMS wallet. Verify calls are free.
Does Resend send a new code?
No. Resend sends the same code again, within 10 minutes of the first send and up to 5 sends in total. Each resend is charged.
Can I change the look of the OTP box?
Yes. Every colour and size is a CSS variable such as --f2s-primary and --f2s-box-size. You can also change any text with the JavaScript API.
Will the code fill in by itself on phones?
Phone keyboards usually offer the code from the SMS because the first box has autocomplete="one-time-code". Chrome on Android can fill it alone only when the SMS ends with a line for your domain, which most DLT templates do not have.
Related guides
- Smart OTP in Fast2SMS: set up OTP on SMS and WhatsApp with fallback
- OTP verification for signup forms: verify mobile numbers before creating accounts
- OTP fraud and SMS pumping: how to protect your OTP form and wallet
- Fast2SMS Resend OTP API: same OTP, 10-minute window, 5 sends
- How to find, view and reset your Fast2SMS API key
- Fast2SMS Smart OTP